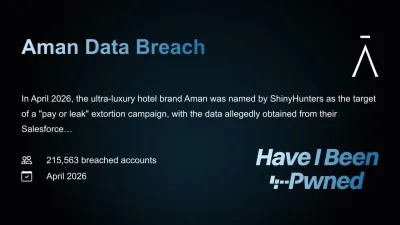
Aman Data Breach Exposes VIP Status and Personal Details of 215,000 Guests
The Aman data breach has exposed the highly sensitive personal information of over 215,000 guests following a 'pay or leak' extortion campaign....
Cybersecurity is the practice of defending computational networks, critical infrastructure, and sensitive data architectures against unauthorized intrusions, malicious exploits, and data compromise. We analyze cryptographic protocols, zero-day vulnerabilities, threat actor vectors, and defensive strategies for robust information security.
The Aman data breach has exposed the highly sensitive personal information of over 215,000 guests following a 'pay or leak' extortion campaign....
Cybersecurity researchers have unearthed the fast16 malware, a highly sophisticated cyber sabotage framework from 2005 that predates the infamous Stuxnet worm....
A former BlackCat ransomware negotiator has pleaded guilty to acting as a double agent, secretly helping the cartel extort his own clients....
The new Anthropic Mythos AI model is terrifying cybersecurity experts by autonomously discovering and exploiting software vulnerabilities faster than human defenders can patch them....
Android banking malware is evolving rapidly, with four newly discovered campaigns actively targeting over 800 financial and cryptocurrency applications globally....
Hackers linked to North Korea are using highly convincing fake Zoom and Microsoft Teams meetings to trick cryptocurrency professionals into installing malware....
A newly discovered security flaw in MediaTek processors allows attackers with physical access to bypass Android lock screens and steal encrypted data in seconds....
A critical zero-day flaw in TrueConf is being actively exploited by state-sponsored hackers to deliver malware through compromised on-premises updates....
Iran-linked hackers successfully breached the personal Gmail account of FBI Director Kash Patel in retaliation for recent DOJ domain seizures....
Security researcher Callum McMahon identified a critical LiteLLM malware attack on PyPI, using Claude AI to analyze and confirm the malicious payload....
Anime streaming giant Crunchyroll is actively investigating claims of a major cyberattack that may have exposed sensitive customer data. The alleged data breach reportedly stems from a malware infection at third-party service provider Telus....
A newly discovered Android malware strain named Perseus is actively targeting popular note-taking applications to steal sensitive user data. Discovered by security firm ThreatFabric, the malicious software hides within third-party IPTV apps to systematically harvest passwords....
Google has officially disabled the widely used Save Image as Type Chrome extension, flagging it as malware for over a million users due to a malicious cookie-stuffing operation....
A massive surge in global cyber threats includes the takedown of 45,000 malicious IPs by Interpol and the rise of AI-assisted ransomware. Critical zero-day flaws in Google Chrome and Apple iOS demand immediate patching from enterprise security teams....
The recent Stryker cyberattack involving Microsoft Intune highlights a severe escalation in state-sponsored digital threats targeting U.S. infrastructure. An Iran-linked hacker group known as the Handala Team has claimed responsibility for crippling the Michigan-based medical technology giant by weaponizing legitimate enterprise management tools....
A massive data breach at U.S.-based Bell Ambulance has exposed the highly sensitive personal and medical information of nearly 238,000 individuals. The Medusa ransomware group has claimed responsibility for the cyberattack, which resulted in the theft and subsequent leak of over 219 GB of critical data....
The FBI is warning consumers about a new wave of doorstep fraud involving unsolicited packages containing malicious QR codes designed to deploy malware....
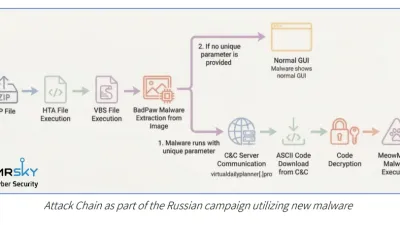
Cybersecurity researchers at ClearSky have uncovered a sophisticated Russian cyberespionage campaign targeting Ukrainian organizations with two newly identified malware families, BadPaw and MeowMeow....
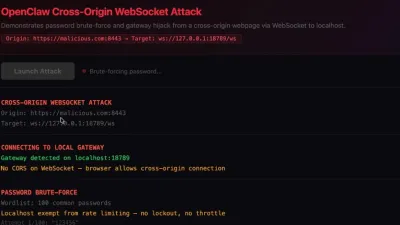
OpenClaw has patched a high-severity vulnerability dubbed 'ClawJacked' that allowed malicious websites to silently hijack locally running AI agents via WebSocket connections....
UpGuard closes a $75 million Series C round to accelerate global expansion and enhance its third-party risk management and attack surface monitoring tools....
A sophisticated threat actor known as GrayCharlie is actively compromising WordPress websites to distribute a potent cocktail of malware, including the notorious NetSupport RAT and Stealc information stealer. By injecting malicious JavaScript into legitimate sites, attackers are turning trusted web pages into launchpads for silent infections....